Checkbox compliance
doesn’t stop adversaries.
We do.
You have to comply with NIS2, DORA or ISO 27001. We meet you where you are: right at the start, in the middle of implementation or after an incident. And we build security with you that withstands attacks, not just audits.

Threat Advisory · November 1, 2026 · TLP:CLEAR

Binance Has the ISO Certificate. North Korea Has the Money.

On October 29, 2026, Binance lost $6.36 billion, most of it in 31 minutes. TRM Labs attributes the Binance hack with high confidence to the North Korean group TraderTraitor (also UNC4899, Jade Sleet, Slow Pisces), whose approach the FBI has described since April 2022. The advisory shows where the group sits in the state, its TTPs in seven acts mapped to MITRE ATT&CK and what an ISO 27001 certificate proves against it.

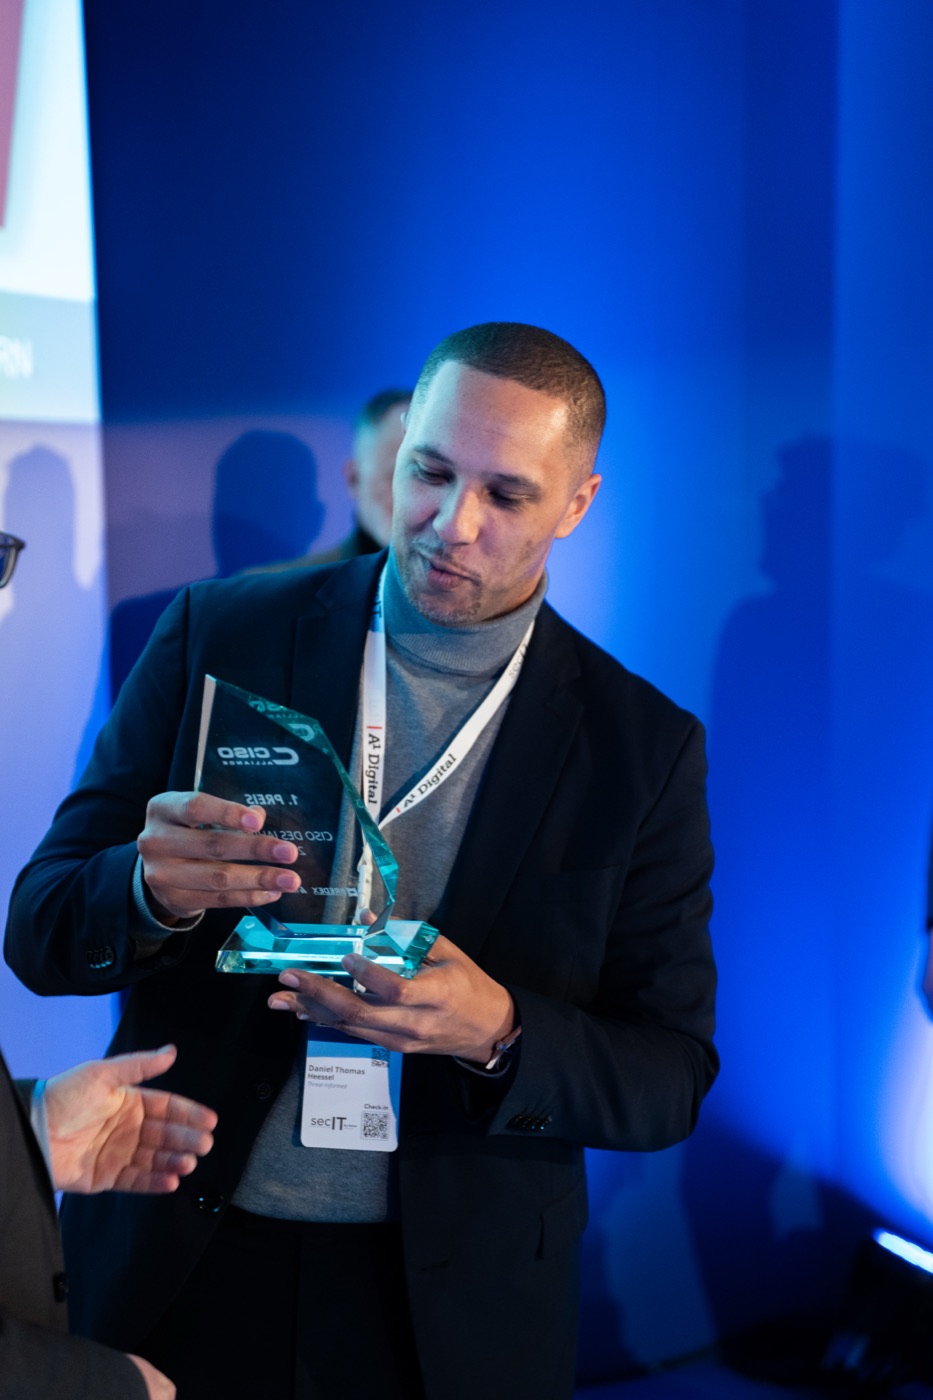
Daniel Thomas Heessel receiving the “CISO of the Year 2026” trophy from the CISO Alliance

CISO of the Year 2026 Award
for Threat‑Informed founder
Daniel Thomas Heessel

Two awards, one line: in 2025 the TOP 10 CISO Award, for introducing Threat-Informed Defense at an international company while personally accountable as CISO. Then in 2026 the next step: CISO of the Year, for Threat-Informed.

This experience sits at your table: someone who knows your role and your constraints from personal accountability, and knows what really protects you in the end.

Get to know us
Audit

We find your gaps. Before others do.

You need an audit because compliance requires it? We do that: by the standard, with traceable documentation, without drama.

You want an audit because you want to know whether you are really secure? That is exactly what we are here for.

Coverage AnalysisControls vs. MITRE ATT&CK
Initial Accesspartial
Executioncovered
Persistencepartial
Credential Accessgap
Lateral Movementpartial
Exfiltrationcovered
Impactgap
Benchmark: your threat profile (industry, region, tech stack).
Illustrative example.
Consulting

Security isn’t something you buy. It’s something you design.

NIS2, DORA, CRA, ISO 27001, TISAX: You know they apply to you. The open question is how to implement them effectively. We align your security with how your adversaries actually operate. Your compliance then becomes the result of effective measures. Not their starting point. From 15 years of responsibility and auditing, we know what holds up in practice. And if the role is missing internally, we take it on: as virtual CISO, ISO or ISB.

Security architectureISMS setupISMS operationDetection & ResponseVirtual ISOVirtual CISO
Threat Intelligence & Threat-Informed Defense

Do you know your adversaries? They already know you.

ISO 27001 (A.5.7), NIS2 and DORA require you to know your threat landscape. We deliver it: 172 adversary groups, 691 techniques and 1,068 mitigations in our data set, prepared for your organization.

And threat intelligence is more than an obligation: if you know who is attacking, you invest only where it counts. In the Quick Check, you can see live who is targeting organizations like yours.

THREAT INTEL172ADVERSARIES691TECHNIQUES1068MITIGATIONS93ISO CONTROLS
Why Threat-Informed

Compliance is an obligation. Threat-Informed is protection.

We have seen how well-documented security can still fail. Audits, policies and certificates create order, but they do not replace a threat picture. Without that threat picture, measures are chosen by checklist, not by impact. That is why our consulting is threat-led: focused on real threats, prioritized, actionable.

„NIS2, DORA and ISO 27001:2022 all require threat-based risk management. But none of them explains how."
– Our approach meets the ISO 27001:2022 requirements for threat intelligence (A.5.7).

Talk to us now, not to the extortionists later.

An initial consultation on your threat landscape, free and without obligation.