Virtual & Interim CISO
Security leadership as a service: we take on strategy, budget responsibility, board reporting and the management of your service providers, either permanently as your virtual CISO or on an interim basis to bridge a vacancy. You buy in C-level leadership that rolls up its sleeves instead of just describing, in exactly the scope your company really needs.
Full responsibility, half a position: the CISO dilemma in mid-sized companies
In most mid-sized companies, information security sits where it historically ended up: with the head of IT, who carries it alongside operations, projects and day-to-day business. That works for a while, but it has structural limits. There is no time for strategy, risk decisions and board reporting, and no distance for a critical view: whoever runs the systems ends up assessing their own work. And without a clear mandate, security remains the topic that always takes a back seat to the next outage.
At the same time, responsibility for information security now lies explicitly with senior management. Section 38 of the BSI Act (BSIG) obliges the management bodies of entities covered by NIS2 to implement the risk management measures and to monitor their implementation; those who fail to do so are personally liable to their own entity under company law. On top of that comes a regular training obligation: management must be able to assess risks and risk management themselves. DORA sets out equivalent requirements for the financial sector. This responsibility stays with you, regardless of how you fill the role. That makes it all the more important who fills it day to day. Small and mid-sized companies in particular need someone in this position who thinks commercially: many security officers demand what the textbook requires without asking what the business can bear. A good CISO knows that money has to be earned before it can be spent, and prioritizes security by what really protects the business. Profiles that master the threat landscape, budgets and boardroom language in equal measure are rare, and in the competition for them, mid-sized companies are up against large corporations and consultancies.
There is also a structural problem: the strategic CISO work of a mid-sized company rarely fills a full-time position. Security strategy, risk decisions, board reporting and vendor management can be handled in a few days per month if they are done consistently. A full-time hire therefore almost inevitably leads to one of two scenarios: either you pay for expensive excess capacity, or the role gets filled up with operational tasks and the leadership work is left undone.
What your own CISO really costs: do the math yourself
The gross salary is only the visible part of the bill. If you want to compare the cost of a full-time hire honestly, you have to look at the full cost:
- Employer social security contributions
- The employer’s share of social security contributions comes on top of every gross salary and, for executive salaries, quickly adds up to a five-figure annual amount.
- Recruiting and vacancy
- Experienced CISOs are almost always hired through executive search firms whose fees are based on the annual salary. Then there is the vacancy period: months in which the role is unfilled while management’s responsibility continues.
- Training, certifications, conferences
- A CISO is only as good as their current threat picture. Certifications, training and conferences are ongoing costs that are included in the hourly rate of a virtual CISO. Then there is what cannot be bought: a virtual CISO learns across many engagements and brings experience from different industries and environments, while an in-house CISO only sees their own organization.
- Absence and wrong-hire risk
- Vacation, illness, resignation: with a one-person role, everything then comes to a standstill. And a wrong hire at C-level costs not only the salary but lost time that nobody can recover in the security program.
- Long-term commitment and employment protection
- A permanent position is a commitment for years: an employed CISO rightly enjoys protection against dismissal, and a separation means notice periods, often a severance payment and months of uncertainty in a sensitive role. An external engagement, by contrast, adapts to demand and ends at the agreed notice period when it no longer fits.
On the other side is the virtual CISO: available immediately, at senior level from day one, billed only for work actually done, scalable when an audit, a project or an incident temporarily requires more capacity, and without the long-term commitment of an employment relationship. Compare both models with your own numbers:
For orientation: depending on scope and tasks, we bill engagements at between €120 and €200 net per hour.
About the defaults: the annual salary of €120,000 is based on mid-sized companies; depending on the source and company size, salary studies cite medians of €90,000 to €160,000 for CISOs in Germany (Robert Half salary overview 2026 and Gallmond CISO salary report 2026, both in German). The 21% corresponds to the average employer share of social security contributions under the 2026 contribution rates (German); above the contribution assessment ceilings, it is effectively lower.
A full-time hire would only be cheaper from about 10 days per month. Until then, you save €8,647 per month.
The calculator runs entirely in your browser: your entries are neither stored nor transmitted to us or third parties. It is a model calculation based on your own assumptions: all values can be adjusted freely, and no hidden factors are included. It assumes 8 hours per day; effects that cannot be quantified, such as vacancy periods, the risk of a wrong hire or downtime, are left out in favor of the full-time hire.
What we take on as your CISO
As your virtual CISO, we take over the leadership role completely, not just in an advisory capacity. We know the objection: then we just have someone who writes documents, and nothing changes. That is exactly what we will not sign up for. For us, paper is a means, never the result: we drive measures through to implementation, sit at the table in vendor negotiations and in the crisis room, check for ourselves whether detection and processes really work, and measure ourselves by impact rather than by the state of the documentation. Hands-on is not a package description for us but the mindset of the whole company. In particular, the role covers:
- Security strategy and annual planning: prioritized by threats instead of following the audit calendar
- Board reporting: risk and status reports in the language of management, prepared so that decisions can be made
- Budget responsibility: justifying and prioritizing security spending and defending it to management
- Vendor management: leading the SOC, MSSP, pentest providers and IT partners with clear requirements
- Crisis readiness: management’s point of contact during a security incident, with a rehearsed escalation path
- Regulators and customers: filling the role verifiably to the outside world, from the customer audit request to the authorities
The model adapts to your situation: permanently as a dedicated virtual CISO with an agreed monthly allotment, or on an interim basis to bridge a vacancy until you have filled the position internally. If you already have an information security officer or a security manager, we lead these roles professionally instead of replacing them. And if you want to fill the role internally in the long term, we build it so it can be handed over: documented, structured and without dependence on us.
Honesty also means saying this: an external engagement does not work against the organization, only with it. We need a reliable point of contact on your side, business units and IT that supply information, and named owners who implement measures in their systems. This cooperation is not small print but the condition for security being created in your company rather than in our folders.
And when things are on fire? That is precisely when the strength of the model shows. In an emergency, a single employee may be on vacation, ill or long gone. In the engagement, we agree on availability for security incidents, and behind your virtual CISO stands our entire incident response experience: threat picture, containment, recovery and communication with regulators, customers and insurers. The incident does not hit you with a one-person defense but with well-practiced reinforcements.
Award-winning leadership, threat-informed
With us, you do not get an anonymous pool of consultants but proven leadership experience: our founder was named CISO of the Year 2026 and held the role for years in an international group of companies, between regulatory requirements, budget reality and technical operations. You buy in this experience on a fractional basis, at a fraction of the cost of a full-time hire.
In substance, we lead according to the approach that shapes our entire company: Threat-Informed Defense. Your security strategy is aligned with the techniques of real adversaries, not with checklists. That makes priorities justifiable, budget decisions defensible and your program measurably more effective. Compliance with NIS2, DORA or ISO 27001 is then the result of good security work, not its purpose.
How to recognize a viable CISO offering
The market for virtual CISOs is growing, and the offerings differ considerably. Before you commit, it pays to take a sober look at five points. They are the same questions by which you may measure us too:
- Regular, visible results
- An engagement that is working leaves traces: status reports, committee meetings, measures that are followed up. If a provider cannot say what you will concretely have in hand every month, you are buying availability instead of leadership.
- Clearly defined scope
- What does the allotment cover, what is commissioned separately, and on what terms? Flat monthly fees without a description of services end either in disappointment or in change orders.
- Clear responsibilities
- Who decides, who supplies, who implements? A serious offering also names what remains with the customer, above all the non-delegable responsibility of management.
- Expertise behind the person
- No individual masters regulation, cloud hardening, detection and crisis management equally. Ask what knowledge your CISO can draw on when things get specialized.
- Deputies and handover
- What happens during vacation, illness or at the end of the engagement? Documentation belongs in your systems, and knowledge must be transferable. Dependence is not a business model but a warning sign.
Our engagement model is built along exactly these points: fixed scope, fixed term, results we can be measured by, and our entire company behind the person.
When a virtual CISO is not the right choice
As convinced as we are of the model, it does not suit everyone. A virtual CISO does not make sense if:
- your organization is so large or so regulated that security leadership is a daily full-time job, with its own security team, its own SOC and a constant presence on site. Then the role belongs in-house; at most, we bridge the time until it is filled.
- you are looking for someone to take responsibility off management’s hands. No CISO can do that, whether in-house or external: NIS2 and DORA explicitly leave this responsibility with management.
- the role in your company mainly means daily operational work: administering systems, handling tickets, supporting users. For that, a CISO is the wrong and too expensive tool; a security manager or a strengthened IT team is a better fit.
- there is no foundation in place yet and the budget for a continuous leadership role is lacking. In that case, a two-day strategy workshop with a prioritized roadmap achieves more than a permanent engagement.
Whether your case is one of them is something we clarify in the initial consultation, openly and without sales pressure. If a different model fits better, we will tell you so and recommend it even if we earn nothing from it.
Frequently asked questions about the virtual CISO
What exactly does a virtual CISO do in our company?
The same as an in-house CISO, just without a full-time position: the virtual CISO is responsible for your security strategy, prioritizes measures and budget, reports to management, steers your service providers and represents the role toward customers, auditors and authorities. You agree on a fixed monthly allotment that can be increased temporarily when needed, for example during an audit or an incident.
We are actually looking for an external ISB, ISO or ISM. Are we in the right place?
Yes. CISO, ISB, ISO, ISM: depending on the company, the standard and the job posting, the same role carries different titles; ISB is the common German term for the information security officer. What is meant is almost always the same: a verifiably assigned responsibility for information security, from strategy through policies and risk reviews to supporting audits and liaising with regulators and customers. That is exactly the role we take on, regardless of what it is called in your company.
How many days per month do we need?
That depends on size, regulation and maturity. In practice, the need for strategic leadership in mid-sized companies is usually in the range of a few days per month; more during build-up phases or projects, less in steady-state operations. We start with an honest estimate of the need and adjust the allotment to reality, in both directions.
Does responsibility still remain with our management?
Yes. Section 38 BSIG explicitly places the obligation to implement and monitor on management, which is personally liable to its own entity for breaches of duty; DORA provides for the same in the financial sector. This ultimate responsibility cannot be delegated. That is exactly why the virtual CISO pays off, because the role makes the responsibility manageable: management receives decision-ready proposals, an honest threat picture and a verifiably managed security process. And we cover the regular training that the law requires of management bodies as part of the engagement.
What does a virtual CISO cost?
Depending on scope and tasks, we bill engagements at between €120 and €200 net per hour. The principle: we do not sell loose hours but an engagement with a fixed allotment and a fixed term, usually one year, whose scope you sign off and we are accountable for. What this means compared with a full-time hire, you can work out with your own numbers in the break-even calculator above: for typical mid-sized needs, the external model is well below the full cost of a full-time position.
Do you simply bill hours like a freelancer?
No, and that is a principle of our company: open-ended hourly billing creates a conflict of interest, because the customer wants to pay for few hours and the consultant wants to bill many. Nothing good comes of that. That is why we work exclusively on engagements: an agreed allotment, a fixed term, an approved scope, and every hour has to justify itself in the result. For us, the hourly rate is the unit of measure for value, not the business model.
Interim or permanent: which fits when?
Interim, when a vacancy has arisen and the role needs to become effective again quickly, for example after a resignation or during an ongoing search. Permanent, when a full-time hire makes no economic sense but you need a continuously filled leadership role. The transition is fluid: some interim engagements turn into a permanent model, and some permanent engagements end in an internal hire that we helped build up.
How quickly can you start?
Much faster than any tender: after an initial consultation on the situation, expectations and engagement, we are usually up and running within a few weeks, and at shorter notice in acute situations. The first weeks are devoted to taking stock: threat profile, ongoing obligations, open risks; after that, the roadmap is set.
Doesn’t a virtual CISO just end up writing concepts?
That concern is justified; there are plenty of engagements that end in documents. Not with us: policies and reports are tools, and we are measured by impact. Specifically, this means that measures are driven through to implementation and followed up, detection and emergency processes are tested instead of just described, and board reporting shows what has really improved, not which documents have been produced. Hands-on is the mindset with which we run every engagement.
When does a virtual CISO not make sense?
If security leadership is a daily full-time job for you, for example because of your size, your own security team and SOC, the role belongs in-house. If the role mainly means operational day-to-day work, a CISO is too expensive a tool. And anyone who hopes to get rid of management’s responsibility this way will be disappointed: legally, it stays with management. In such cases, we recommend the more suitable model in the initial consultation, from a strategy workshop to an interim bridge.
An employee would always be there. An external one would not, right?
Often the opposite is true: a single internal role is completely unfilled during vacation, illness or resignation, and incidents happen anyway at exactly those times. In an external engagement, we explicitly agree on availability for emergencies, and in an incident it is not one person but our company with its incident response experience that stands behind you. With the external model, predictable availability is a contract clause; with an employee, it is a wish.
Doesn’t this make us dependent on you?
No, if it is set up correctly, and that is exactly how we set it up: strategy, decisions and processes are documented in your systems, not in ours. Policies, risk registers and reporting belong to you. If you later want to fill the role internally, we hand over in an orderly manner and, if you wish, support your successor during onboarding.
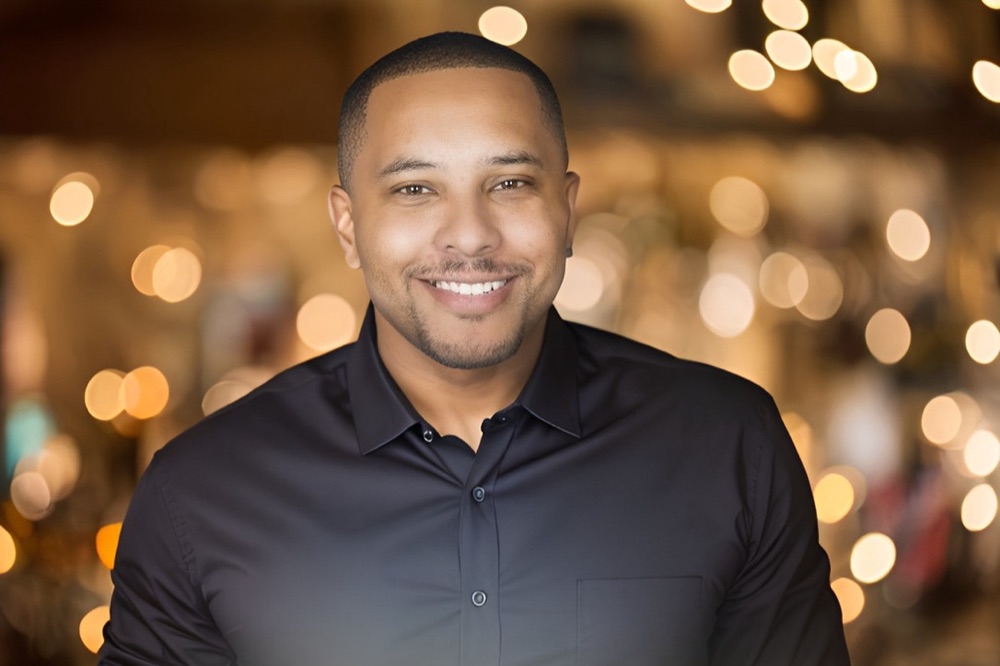
Daniel Thomas Heessel was named CISO of the Year 2026 and, as the security lead of an international group of companies, brought regulatory requirements and technical reality together. Daniel is a certified ISO 27001 Senior Lead Auditor, CISSP, CISM and MITRE ATT&CK Defender.
As of September 2026. Governance obligations verified against Section 38 BSIG (gesetze-im-internet.de, German), Art. 20 of Directive (EU) 2022/2555 and Art. 5 of Regulation (EU) 2022/2554 (EUR-Lex).